
Ransomware/Threat Intelligence
Expedia Confirms Supply Chain Breach as n0n Extortion Group Claims Nearly 1 Billion Traveler Records
Expedia Group has confirmed a cyberattack after a newly formed Russian extortion group called n0n claimed it stole data on nearly one billion travelers from the world’s second-largest online travel agency. Expedia told Skift on Thursday that the attackers reached its systems through a compromised third-party data platform provider, in a supply chain attack that also affected several other companies.
What Expedia has confirmed
- Attackers got into Expedia’s systems through a compromised third-party data platform provider, using that provider’s trusted access.
- The same supply chain attack affected multiple companies.
- Expedia says it acted to contain the attack as soon as it became aware of it and brought in outside cybersecurity experts to investigate.
- Expedia says its platforms remain safe for travelers and business partners.
- Expedia has not confirmed the data volumes n0n claims, and its investigation is ongoing.
What n0n claims to have stolen
| Data type | Claimed volume | Contents |
|---|---|---|
| Loyalty program records | 830+ million (from 35 programs) | Email addresses, membership IDs, points balances |
| Consumer account and credential records | 333+ million | Account data with password-like tokens (hashed) |
| Consumer matching records | 72 million | Not specified |
| Traveler profiles | 58 million | Home airports and account information |
| Credit card spending records | ~2.5 million | Linked to hashed email addresses |
| Guest records | 500,000 | Accommodation details |
| Source code | Not specified | Allegedly taken using live credentials found in the same breach |
How the attack happened: a stolen Qubole key
According to cybersecurity firms Wiz and Sentra, the attackers used a stolen vendor key from Qubole, a Google Cloud Platform partner. The key gave them a trusted path into Expedia’s big data platform. Expedia has not publicly named the vendor.
Leak site now lists Expedia as “Not paid — leaked”
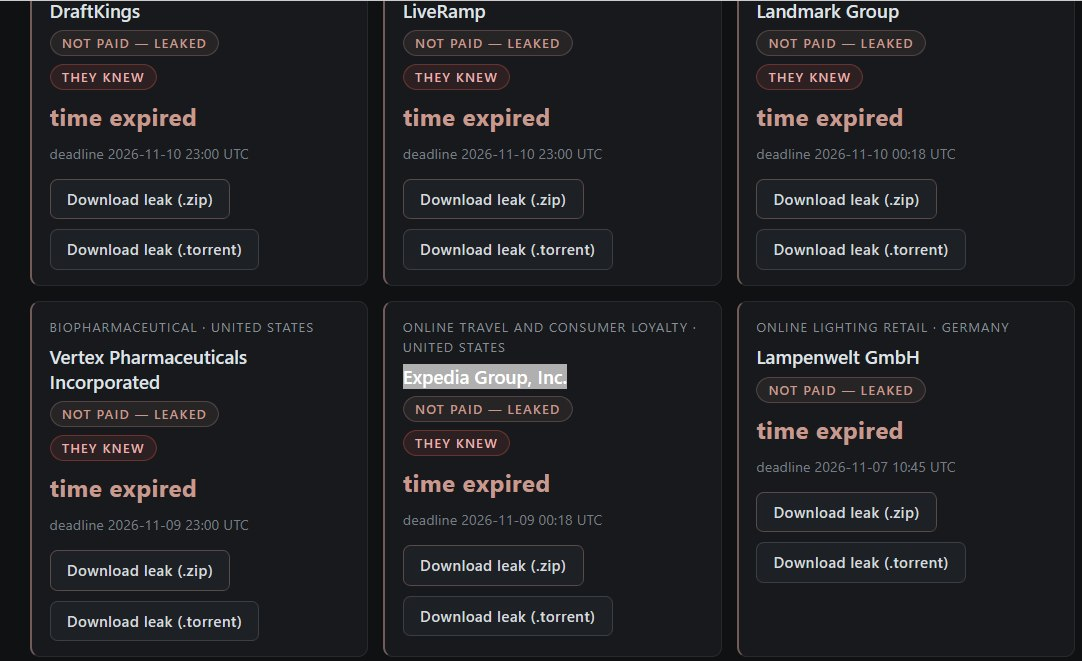
n0n’s leak site now shows Expedia Group with the labels “NOT PAID — LEAKED” and “THEY KNEW”. Its countdown deadline (November 9, 2026, 00:18 UTC) has expired, and download links for the alleged data are posted in .zip and .torrent formats. The same page lists other organizations, including DraftKings, LiveRamp, Landmark Group, Vertex Pharmaceuticals, and Lampenwelt GmbH, with the same “not paid — leaked” status. We have not verified the published data or confirmed that those other listings are linked to the same supply chain attack.
Who is n0n?
- Emerged: mid-September 2026
- Origin: Reportedly Russian
- Model: According to SOCRadar, n0n focuses on data theft and extortion without using ransomware
- Scale: Its leak site claims 224 attacks since September
The group uses an unusual pressure tactic. New victims appear on its leak site only as numbered entries, such as “Company 89” or “Company 90,” with a countdown timer labeled “pending exposure.” A company is only named if it doesn’t pay before the deadline. Ransom negotiator Alex Waintraub, who isn’t working on the Expedia case, told Forbes that n0n’s claims appear designed to pressure victims into paying. Expedia’s decision to confirm the breach publicly is unusual under this model, and it may weaken the group’s leverage.
Why it matters
Expedia reported $14.7 billion in revenue in 2025 and also runs Hotels.com, Vrbo, Travelocity, Orbitz, Hotwire, and Trivago. Customers with Expedia, Hotels.com, or Vrbo accounts may all be in the same data pool. The incident also shows the growing risk of supply chain attacks on cloud data platforms: one stolen vendor key can give attackers trusted access to many organizations at once.
Recommendations for travelers
- Change your password for Expedia, Hotels.com, and Vrbo accounts, using a trusted device.
- Don’t reuse passwords: If you used the same password elsewhere, change it there too. The stolen tokens are hashed, but attackers may still be able to crack them.
- Watch for phishing: With email addresses, membership IDs, and points balances in hand, attackers can write very convincing loyalty-themed messages. Be wary of emails about “expiring points” or “account verification.”
- Enable multi-factor authentication wherever it’s offered.
- Monitor loyalty accounts for unexpected point redemptions or changes.
Recommendations for organizations
- Audit third-party access to cloud data platforms, especially long-lived vendor keys and cross-account access.
- Rotate keys and credentials shared with data platform vendors, and check whether any were exposed.
- Review the Wiz and Sentra research on the Qubole attack, and hunt for signs of the same activity in your own environment.
- Scan data platforms for embedded secrets: n0n claims it took source code using live credentials it found inside the compromised environment.


